preferred on

Points of Focus
- Claude-supplied malicious links are now being used to steal crypto credentials.
- Refi Hub co-founder Numa Lunah reported a compromise after following one link.
- Microsoft has separately tracked AI-poisoned links delivering malware through chatbot responses.
Crypto users are facing a new attack vector as malicious software links begin appearing inside AI-generated answers, turning trusted chatbot recommendations into potential routes for credential theft and wallet compromise.
The latest warning followed an incident involving Refi Hub co-founder Numa Lunah, who said his computer was compromised after he followed a download link supplied during a Claude conversation. Lunah was attempting to install transcription software when the AI assistant reportedly directed him to what appeared to be a legitimate download page but was instead a copycat site distributing malware.
After wiping and rebuilding the affected machine, Lunah said he found a malicious “SKILL.md” configuration file in his Claude Code environment. The file was designed to silently download malware again and steal credentials, meaning reinstalling the operating system alone might not have removed the attack path if the poisoned configuration was restored.
This is why i don’t blindly trust anything just because AI recommended it
Claude users are being targeted with malware disguised as normal downloads
One victim got infected through a link inside a Claude chat
Then a fake SKILL.md file helped the malware reinstall itself
29… pic.twitter.com/Rgsq7qjowp
— Justin Wu (@hackapreneur) August 30, 2026
AI recommendations are becoming another malware distribution channel
The attack is more concerning for crypto users because credentials stored on an infected computer can include exchange sessions, wallet information, API keys, and other secrets capable of giving an attacker access to digital assets.
Microsoft has already documented the broader technique.
In May, Microsoft Defender researchers disclosed a campaign in which attacker-controlled software-download sites were promoted through both poisoned search results and recommendations generated by AI chatbots. Researchers identified more than 150 malicious domains impersonating legitimate system utilities.
Microsoft said telemetry showed users being directed toward malicious domains after interactions with large language models, although it cautioned that the evidence did not establish a systemic flaw in any particular chatbot.
The malware campaign initially focused on cryptojacking, targeting users with high-performance GPUs, but also installed persistent remote-access software capable of supporting later data theft or additional malware deployment.
The attack model changes a familiar security assumption. Users have traditionally been warned to distrust advertisements, unsolicited emails, and suspicious search results. An AI assistant can feel different because the link appears inside a conversation generated specifically in response to the user’s question.
That perceived trust can make a poisoned recommendation particularly effective.
Fake Claude downloads have already targeted crypto wallets
Claude’s popularity has separately made the brand a recurring lure for malware campaigns.
In April, Bybit’s security team uncovered a macOS campaign targeting people searching for Claude Code. Attackers used search-engine optimization poisoning to push a fake installation page toward the top of search results, leading victims into a multi-stage infection designed to harvest credentials and target cryptocurrency assets.
Another campaign identified by security researchers used fake Claude Code installation pages to distribute malware capable of stealing API keys, authentication tokens, developer credentials, and crypto-wallet information. Researchers identified more than 88 fraudulent domains impersonating Claude and other developer services.
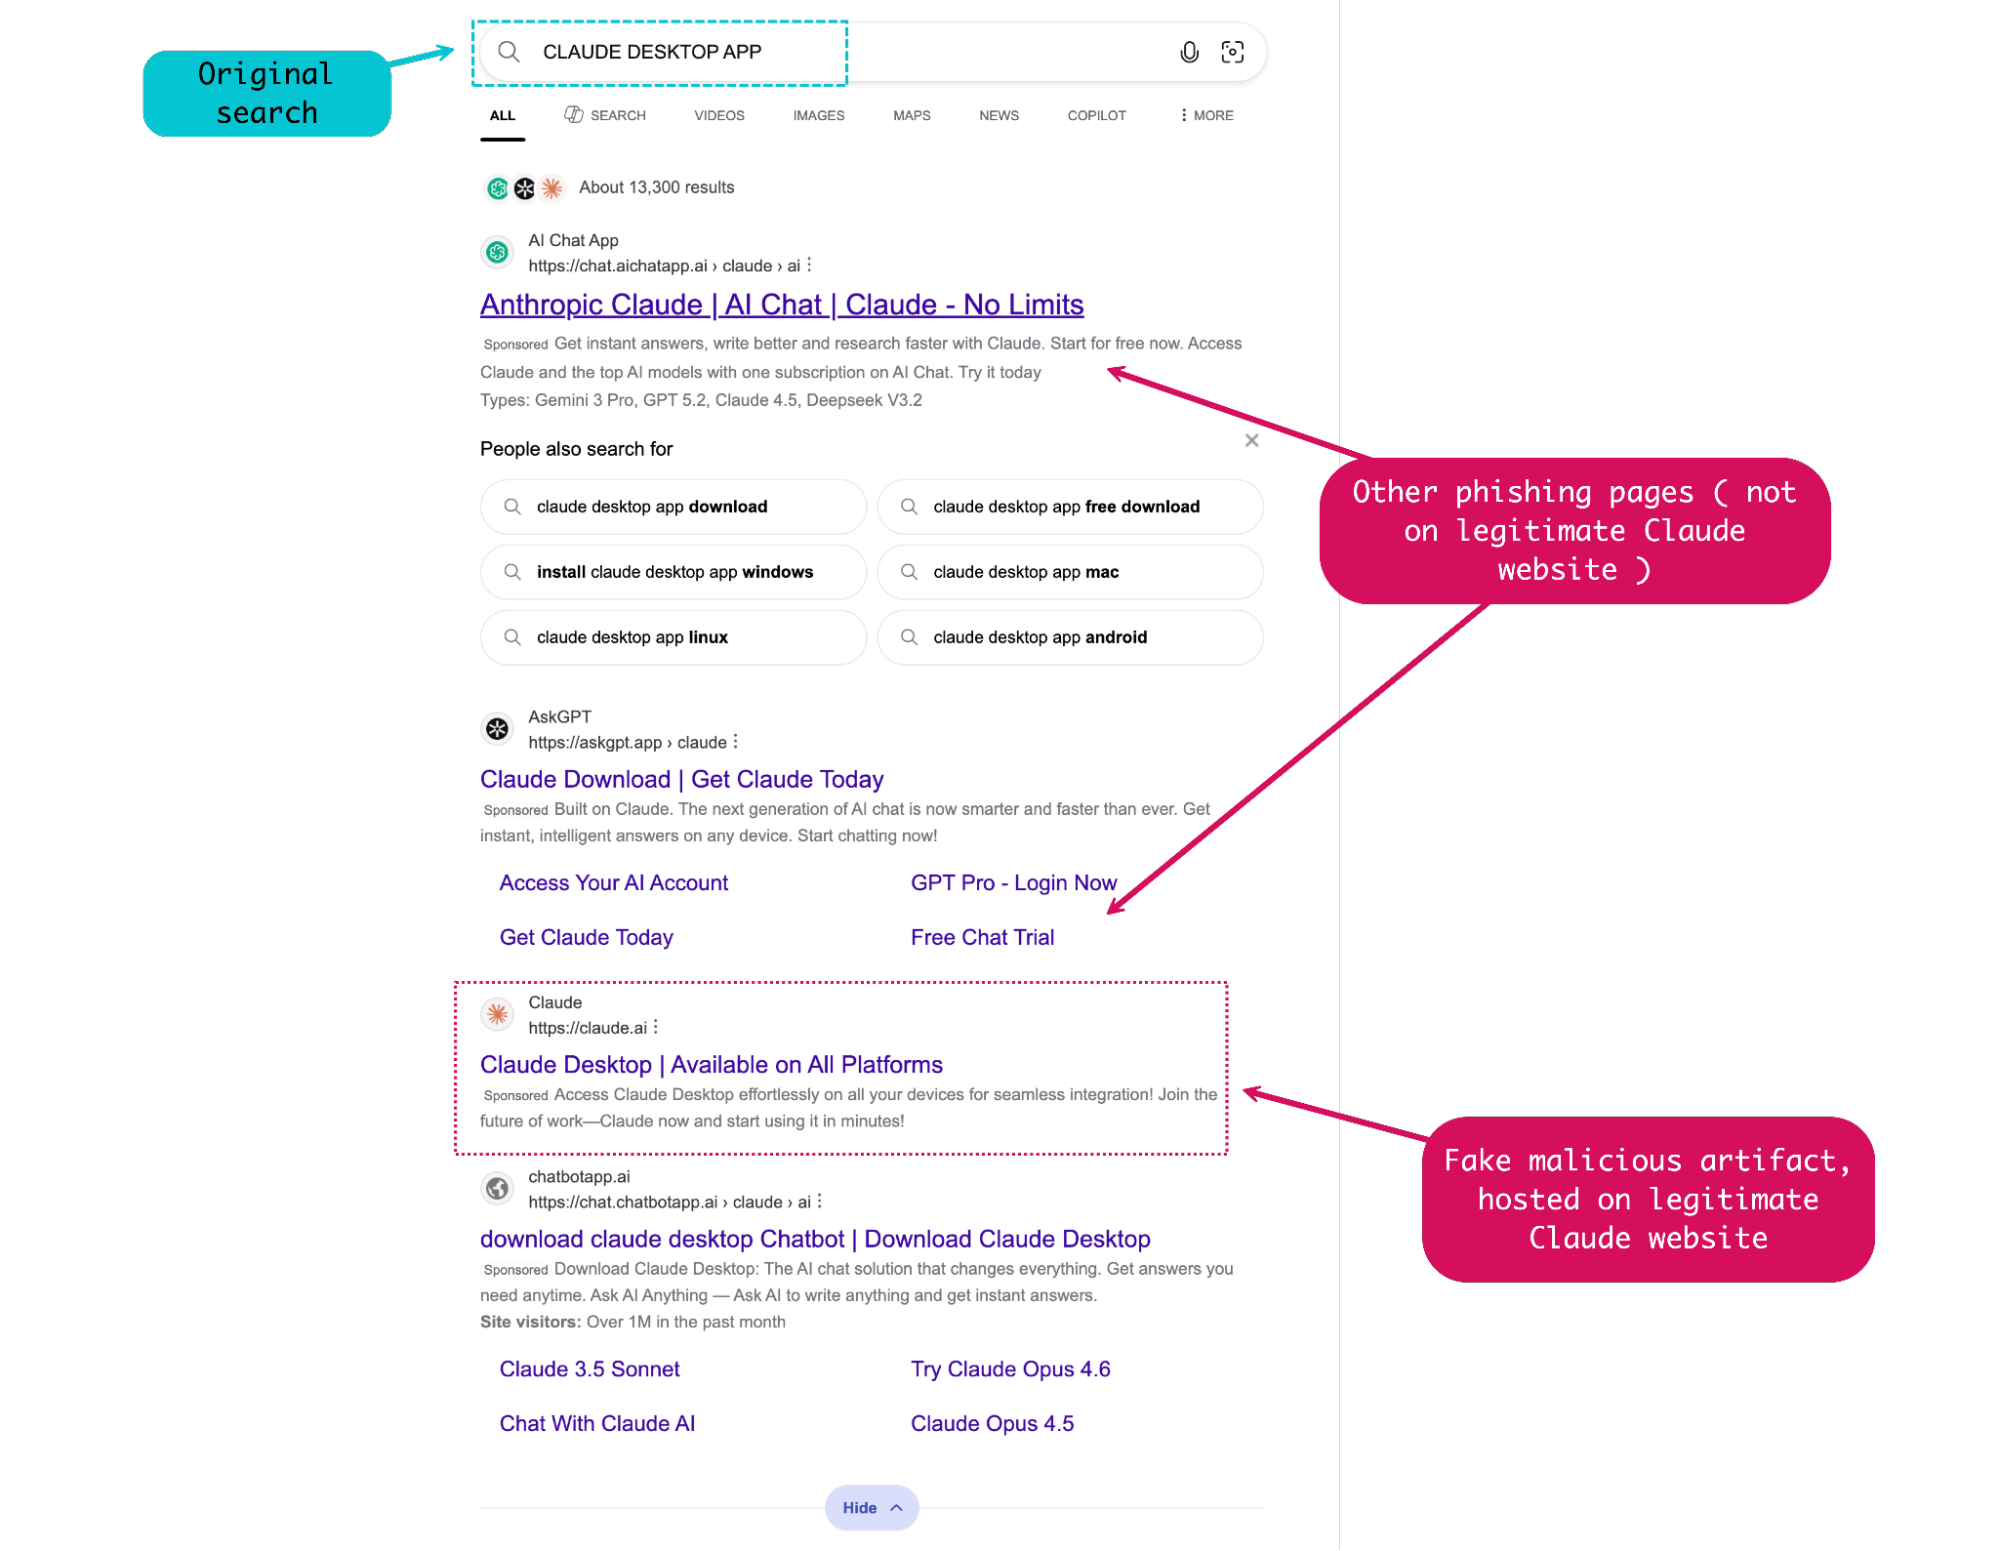
Huntress subsequently documented an even more direct abuse of Claude infrastructure. During its FakeAgent investigation, victims searching for the Claude desktop application were sent to a malicious public Claude Artifact hosted on the genuine Claude domain. The resulting malware campaign affected 29 organizations and deployed SectopRAT, a remote-access trojan capable of stealing passwords, personal information, files, and credit-card data.
Crypto makes stolen credentials unusually valuable
For most users, an infostealer can compromise passwords and browser sessions. For someone working in crypto, the same infection can reach assets that are far harder to recover.
Exchange API keys may permit trading or withdrawals depending on their permissions. Browser cookies can expose active sessions. Locally stored wallet data can become another target, while a stolen seed phrase or private key can give an attacker irreversible control over funds.
Microsoft has also observed attackers using Claude branding directly for credential theft. An April phishing campaign targeting users across more than 2,000 organizations impersonated Anthropic services and attempted to intercept login credentials and authentication tokens.
None of these incidents means Claude itself has been broadly compromised. They show something different: Attackers are exploiting the trust users place in AI brands, AI-generated recommendations, and links surfaced inside chatbot workflows.
For crypto users, that changes a basic security habit. A link appearing inside an AI answer cannot automatically be treated as safer than one appearing in a search result. When downloads may gain access to a machine holding wallets, exchange sessions, or API credentials, verifying the software against the vendor’s official domain before executing it has become part of crypto operational security.