preferred on

Points of Focus
- Coinbase confirmed customer contact data exposure through Amplitude but said its systems and customer funds were unaffected.
- SlowMist’s claim that over 70,000 users were affected remains unverified, with Coinbase withholding the actual count.
- New York cybersecurity rules require vendor oversight, but no regulatory violation has been established in the Amplitude incident.
Coinbase said late on Oct. 27 that a security incident at analytics vendor Amplitude affected contact details for a limited group of customers.
The exchange denied having suffered a data breach. It said it had found no sign of unauthorized access to its systems and that customer funds were unaffected. An executive at blockchain security company SlowMist put the number of affected users at over 70,000, while Coinbase’s statement gives no count.
Coinbase has not had a data breach.
Amplitude, an analytics vendor, experienced a security incident which impacted a small subset of Coinbase customer contact data, among other Amplitude customers.
We’ve found no evidence of unauthorized access to Coinbase systems, and…
— Coinbase Support (@CoinbaseSupport) October 28, 2026
What Coinbase’s statement leaves unanswered
Coinbase said the incident also touched other Amplitude customers and that it is notifying affected users and regulators as its legal obligations require. The statement gave no customer count, no list of exposed data fields, and no date or duration for the incident. It also did not say who was responsible for the incident.
Amplitude sells product analytics, session replay, and heatmap tools. Its public status page showed no notice about the incident as of Oct. 28.
Contact data can feed phishing and social engineering attempts even when passwords and funds stay untouched. In a similar incident earlier this year, Trezor said in an Aug. 13 notice that a breach at logistics partner ShipMonk exposed customers’ names, phone numbers, email addresses, and shipping addresses. Trezor warned that scammers could use the data for fake emails, calls, and letters.
A 70,000 figure from one security executive
The estimate traces to 23pds, a SlowMist partner and chief information security officer. He said hackers obtained contact details for more than 70,000 users, and he hadn’t yet confirmed whether passwords or funds were taken. Another follow-up post noted that many project teams use Amplitude.
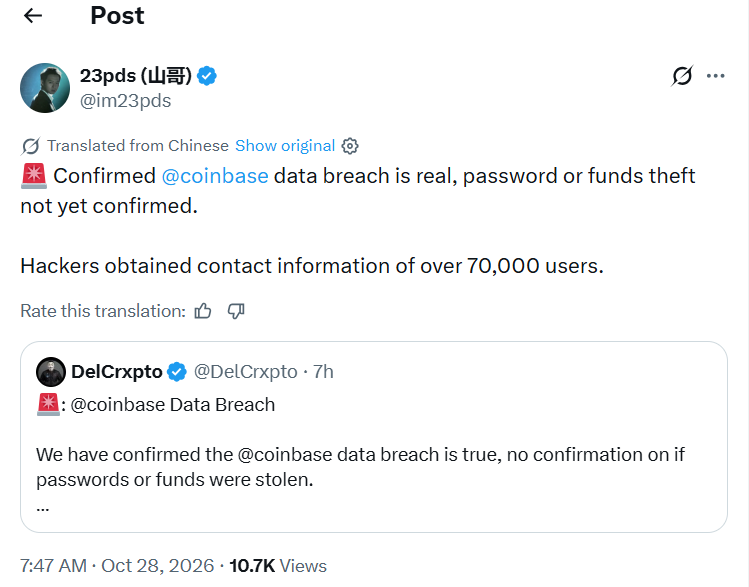
Coinbase’s description of a limited group gives no number against which that claim can be tested. Polygon Labs chief technology officer Mudit Gupta answered Coinbase’s post by arguing that customer data counts as breached, no matter how it was exposed.
So you had a data breach. Don't be coindcx.
Your customer data got breached, it doesn't matter how.
— Mudit Gupta (@Mudit__Gupta) October 28, 2026
In a May 15, 2025, US Securities and Exchange Commission filing, Coinbase said a threat actor appears to have paid overseas support contractors or employees for customer data. A Maine attorney general filing lists 69,461 people affected. The data included names, contact details, government ID images, and masked Social Security digits. Coinbase said it was strengthening anti-fraud protections against possible social engineering use of the data. Coinbase preliminarily estimated costs of $180 million-$400 million.
New York rules hold regulated firms responsible for vendor oversight
An Oct. 21, 2025, letter from the New York Department of Financial Services (NYDFS) restated that regulated companies cannot delegate cybersecurity compliance to outside vendors. The letter says it adds no new requirements and covers due diligence, contracts, monitoring, and termination.
That said, the Amplitude incident alone doesn’t establish a violation. The regulation defines nonpublic information about individuals as personal data paired with identifiers such as Social Security numbers, account numbers, or biometric records. It is not established whether the exposed details qualify or which Coinbase entity was involved. NYDFS lists Coinbase, Inc with virtual currency and money transmitter licenses granted in January 2017.
The story remains developing as of Oct. 28, 2026, with Coinbase yet to disclose the complete details.