preferred on

Points of Focus
- Harmony’s rollback puts blockchain immutability to the test: the exploit and subsequent rollback demonstrate the difference between a blockchain being technically difficult to alter and a network collectively deciding to reject part of its own history.
- Not all hack ‘reversals’ are equal: voluntary returns, asset freezes, and true blockchain rollbacks show the difference between recovering stolen funds and changing a chain’s canonical state.
- The governance problem behind Ethereum’s DAO fork and Harmony’s response highlights the risk that emergency rollbacks create moral hazard while absolute immutability can leave a network permanently trapped.
Blockchains are meant to be immutable. Once a transaction has been validated, included in a block, and buried beneath subsequent blocks, it becomes part of the permanent record. No bank administrator can log in and reverse it. No central authority can press an undo button.
The idea of immutability was key to the founders of the crypto economy and remains essential to the related idea of crypto decentralization. If the blockchain is unchangeable, then transactions can’t be rolled back or overturned at the whim of a bank manager, financial institution, or government.
But recent developments complicate the immutability issue.
Harmony ONE: Open blockchain suffers major hack
In August 2026, after an attacker exploited a cross-shard vulnerability to create more than 3 trillion unauthorized ONE tokens, Harmony concluded that targeted cleanup was no longer practical. Its proposed solution was to roll affected shards back to a point before the exploit, discarding the subsequent blockchain history and rebuilding from a clean state.
But if a blockchain community can collectively decide to erase a section of history after a sufficiently serious hack, what does “immutable” actually mean?
Blockchain immutability is real, but it has always been more conditional than any marketing slogan suggests. Cryptography can make records extraordinarily difficult to alter unilaterally, but there have always been ways to work around that limitation.
A blockchain cannot normally reach backward and delete history, but the people who secure it can sometimes decide to stop recognizing that history.
Harmony’s crisis is part of a much older argument, one that stretches back to the Ethereum DAO fork of 2016, the birth of Ethereum Classic, and subsequent debates over whether lost or stolen assets should ever be recovered through protocol-level intervention.
What happened to Harmony?
Harmony first confirmed an exploit on Aug. 12, 2026, after detecting unauthorized minting of its native ONE token. Initial reports suggested that roughly 4 billion ONE had been created. That figure turned out to be only the beginning of the problem.
The attacker created new tokens, but the underlying vulnerability also allowed valid cross-shard receipts to be processed repeatedly. In effect, the same proof of value moving between shards could be replayed, creating a credit without a corresponding debit elsewhere in the system.
In the immediate aftermath of the attack, the new ONE tokens immediately began moving to new wallets and throughout the system. One forged mint wallet moved 2.385 billion ONE in 106 seconds.
That left Harmony scrambling for a response. The rapid distribution of new tokens made that challenging. While stolen assets can sometimes be identified and frozen, an unauthorized token that has been repeatedly moved through wallets, decentralized exchanges, liquidity pools, and bridges becomes much harder to isolate.
Harmony reportedly considered several alternatives:
- Burning the forged tokens
- Blacklisting affected addresses
- Selectively unwinding transactions
- Migrating to a replacement ONE token.
Once forged tokens had entered legitimate pools and services, a targeted recovery risked punishing users who had unknowingly interacted with the contaminated assets. Burning tokens from known attacker wallets would not necessarily remove all of the counterfeit supply. Blacklisting could leave the economic damage embedded elsewhere in the system.
Harmony’s conclusion was that a single rollback window — returning the affected shards to a state immediately before the first confirmed unauthorized mint — was the least risky and most consistent option. The price of that decision is obvious: Legitimate transactions occurring after the chosen rollback point would disappear alongside the attack.
To remove the malicious history, the network also needed to remove some legitimate history.
A blockchain rollback is not the same thing as pressing “undo”
A blockchain rollback is usually not a centralized administrator editing out old blocks. The old blocks still exist. Nodes, archives, and block explorers may retain copies of them. What changes is which version of history the network agrees to recognize as canonical.
A simplified version looks like this:
- Old chain: A → B → C → D → E → Hack → F → G → H
- Recovery decision: Nodes agree that history after a particular point should no longer be canonical.
- New canonical chain: A → B → C → D → E → F’ → G’ → H’
Instead of altering the cryptographic hash of the old blocks, validators and nodes adopt software or procedures that establish a different canonical state. In doing so, the network demonstrates two layers of blockchain immutability.
1. Technical immutability
Within a functioning consensus system, altering an old block is extremely difficult.
Each block is linked cryptographically to the previous one. Changing historical data changes the block hash, which breaks the chain of references. An attacker attempting to rewrite history must also overcome the network’s consensus mechanism.
That is what gives blockchain records their resistance to unilateral manipulation.
2. Social immutability
Technical protections do not prevent the entire network from changing its rules.
The protocol itself is software. Nodes choose which software to run. Validators choose which chain to validate. Exchanges choose which asset and chain to support.
If a sufficiently large and economically important portion of the ecosystem agrees to adopt a new version of the rules, the network can move to a new canonical history.
Harmony’s problem was especially severe because the ledger itself was compromised
There is an important difference between an application being hacked and the accounting logic of the blockchain itself failing.
Consider the archetypal decentralized finance (DeFi) exploit: The DAO hack of 2016.
Back then, especially, code was law. A poorly written smart contract contained a vulnerability, and a hacker raced to drain the decentralized autonomous organization (DAO) of millions of Ether. The Ethereum blockchain processed every transaction correctly. The protocol did exactly what the smart contract told it to do. The failure came when it was told to do something incorrectly.
Harmony’s August 2026 incident appears similar. The reported vulnerability involved cross-shard receipt verification, allowing receipts to be replayed and new ONE to be created without the corresponding debit required to preserve the intended supply. It was a flaw in the code, and one that resulted in a huge wave of new ONE supply, crashing the token’s value.
Faced with the flaw in the code, Harmony opted to deploy a variation of the same solution used by The DAO back in 2016: rewinding the canonical blockchain to a time before the fork.
Ethereum and The DAO
In 2016, at block 1,920,000, Ethereum implemented what was formally described as an “irregular state change,” transferring Ether (ETH) associated with The DAO and its child contracts into a recovery contract from which affected holders could withdraw.
According to Ethereum Improvement Proposal 779, The DAO fork did not fundamentally change Ethereum’s transaction format, block structure, or Ethereum Virtual Machine instruction set. Instead, it made a specific alteration to the blockchain’s state by moving funds from a defined set of accounts into a recovery mechanism.
Ethereum’s own historical documentation describes The DAO fork as a response to an insecure contract from which more than 3.6 million ETH had been drained. The decision was supported by a majority of participants, but opponents refused to recognize the altered chain. They continued the original blockchain, which became Ethereum Classic.
The economic and social majority adopted one history, while a minority continued to recognize another.
Practically, Ethereum undid The DAO hack, but not through any technical editing of the fundamental code, just the consensus of a majority of validators on the network. Then, as now, that remains one possible way of dealing with a network hack.
There are at least four different ways a “hack reversal” can happen
Crypto hacks always prompt discussions of how to reverse the issue. There are four common ways.
1. The attacker voluntarily returns the funds
In August 2021, an attacker exploited Poly Network and stole about $612 million in crypto assets. Almost immediately, the attacker began returning the funds through ordinary onchain transactions.
Poly Network ultimately announced that it had recovered the remaining 28,953 ETH and 1,032 WBTC after the individual behind the attack provided access to the final multisig wallet. Poly Network said that all user assets transferred out during the incident had been recovered.
2. A centralized intermediary freezes or recovers assets
The Ronin bridge hack, one of crypto’s largest, resulted in nearly $630 million in assets stolen — mostly ETH. A small percentage, roughly $30 million or so, was recovered via law enforcement efforts, crypto industry players, and frozen assets.
But overall, the percentage was minuscule, highlighting just how resistant a decentralized system is to outside intervention.
3. An application or smart contract performs its own recovery
In July 2023, vulnerabilities affecting certain versions of the Vyper programming language contributed to exploits against several Curve liquidity pools and associated DeFi protocols.
Some of the affected assets were recovered through a combination of white-hat intervention, voluntary returns by the exploiters, and subsequent governance-based compensation; the white-hat maximal extractable value operator “c0ffeebabe.eth” recovered and returned 2,879 ETH to Curve after front-running an attacker.
4. The network changes canonical history or performs an irregular state change
This is the Harmony and The DAO category. The protocol’s operators collectively adopt new rules or a new state that changes the practical outcome of historical events.
This is the most consequential form of intervention because it reaches beyond a single application and into the infrastructure itself. The deeper an intervention goes, the greater the governance question becomes.
While the other reversal methods apply above the fundamental blockchain level, this method changes reality at the level of the chain the network recognizes as canonical.
Rollback expectations risk a moral hazard
There is a serious argument against using protocol-level recovery too readily. If users, developers, and investors begin to assume that catastrophic losses will be reversed, incentives change.
Today, a network rolls back after a protocol-level vulnerability creates trillions of counterfeit native tokens.
Tomorrow, why not after a $10-billion DeFi exploit? Or a major bridge failure? Or the collapse of a politically important stablecoin? Or the loss of funds belonging to a major institution?
Once a network establishes that history can be changed for sufficiently important losses, every future victim has an incentive to argue that their loss was sufficiently important, too.
Absolute immutability has its own dangers
The opposite position is not cost-free either. Both Ethereum, in The DAO attack, and Harmony, with the ONE exploit, decided that the costs were simply too high to bear.
Ethereum went on to achieve great success as a blockchain and a token, currently boasting a nearly $300-billion market cap as the second-largest token.
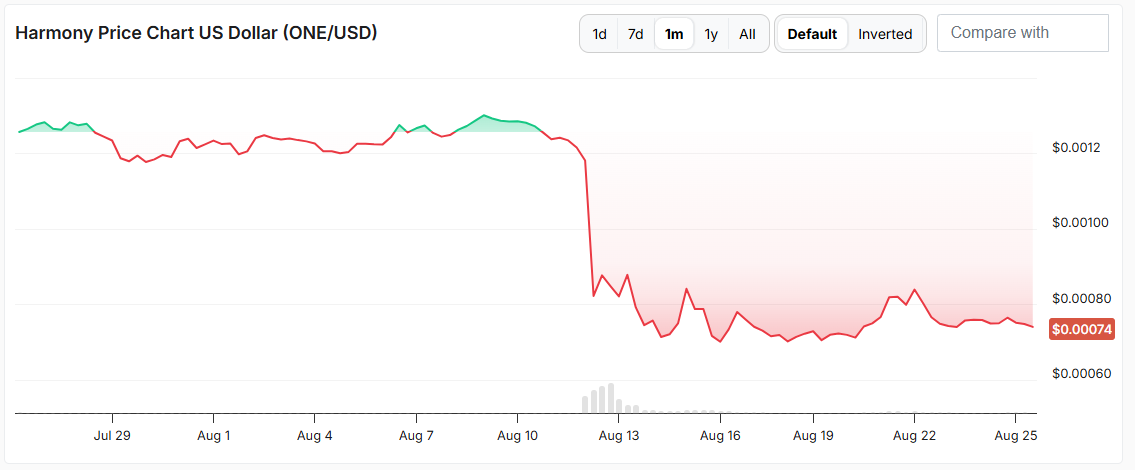
Harmony hasn’t recovered from the attack’s aftermath; the token plummeted from $0.00123 to $0.00073 and hasn’t bounced back yet. The ultimate protection against arbitrary blockchain governance is the ability to fork or, in Harmony’s case, to roll back the blockchain.
Decentralization does not remove politics
The Harmony incident highlights one of the industry’s most persistent misconceptions: that decentralization is the elimination of governance.
When the protocol itself fails, someone must still decide what the network should do.
In Harmony’s case, the decision wasn’t without detractors, with some users wanting a simple burn of the minted tokens, while others complained that the rollback seemed to have no impact on token price.
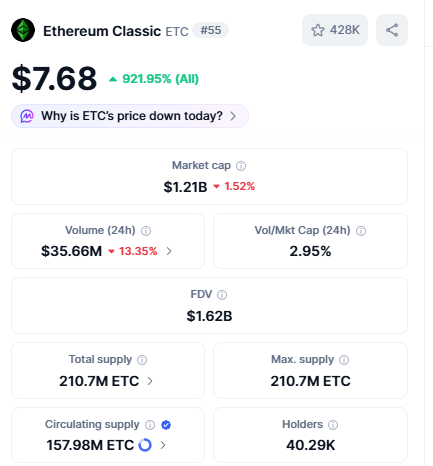
And of course, that happened with Ethereum and The DAO hack; it’s the very reason that Ethereum Classic exists.
Can a blockchain undo a hack?
Yes — but not simply and not without major consequences.
A blockchain cannot normally reach into its own past and silently edit a transaction; there’s rarely an “undo” button.
But a blockchain is also a living consensus system, and if enough of the network agrees to adopt new software, reject a portion of the previous history, or perform an irregular state transition, the ecosystem can establish a new canonical reality.
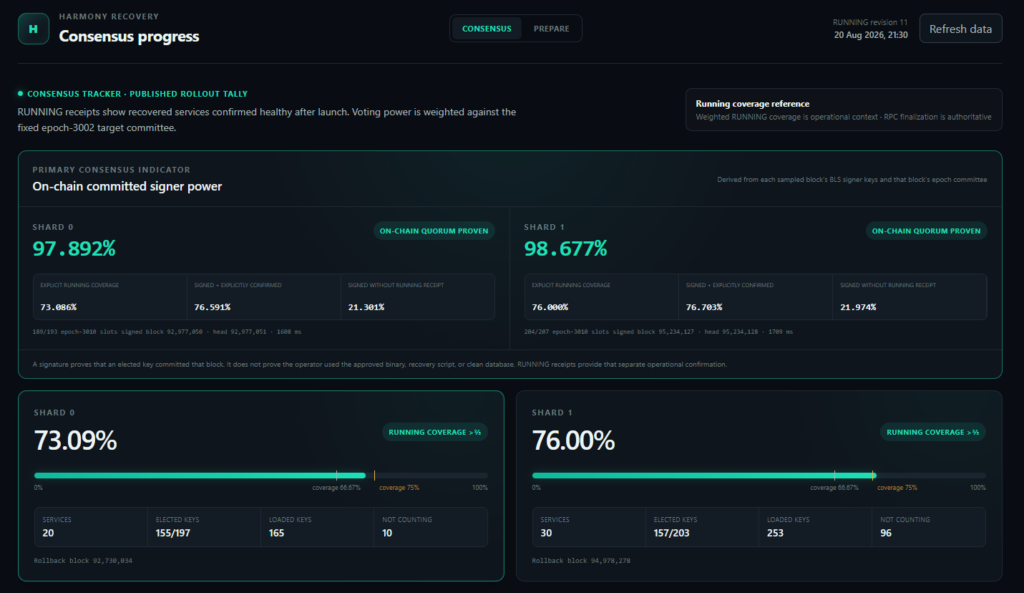
That is the logic behind Harmony’s proposed recovery.
Blockchain history is extremely difficult to change without consensus. It is not impossible to replace through consensus.
Harmony’s case may ultimately be viewed as another example of the legitimate use of that power, on a smaller scale but similar in nature to Ethereum’s hard fork. In both cases, the fundamental issue is more complicated than whether “blockchains are immutable” or not. Blocks are cryptographically linked, but legitimacy is socially negotiated.